CVE-2018-19981 | BDVDB-2026-114709 Detail
Description#
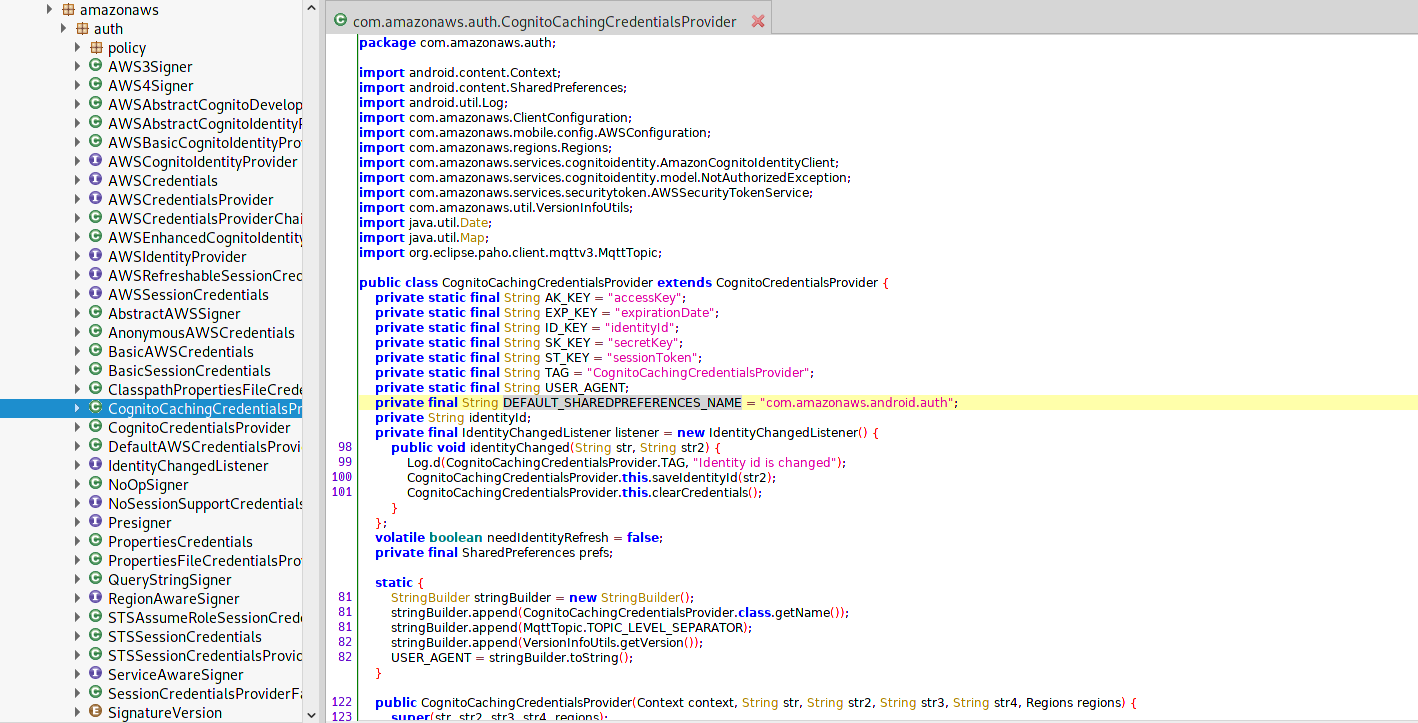
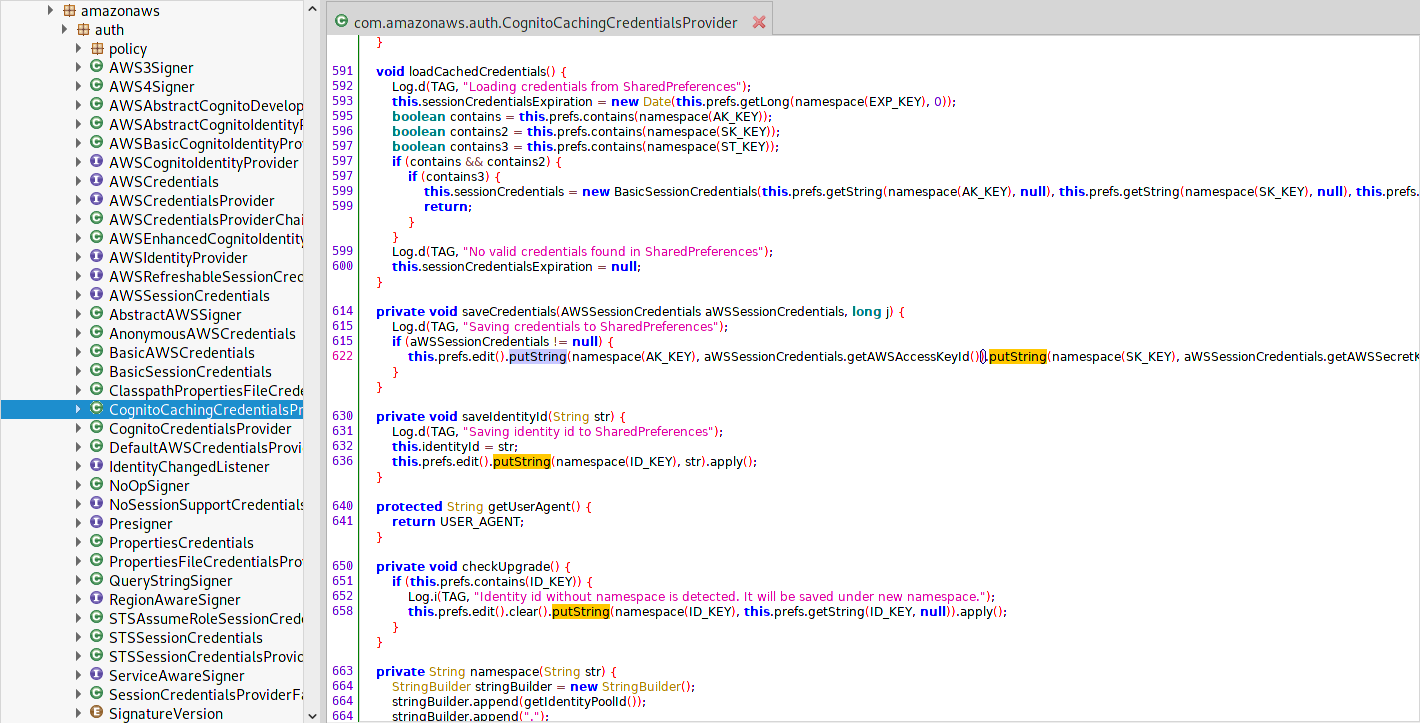
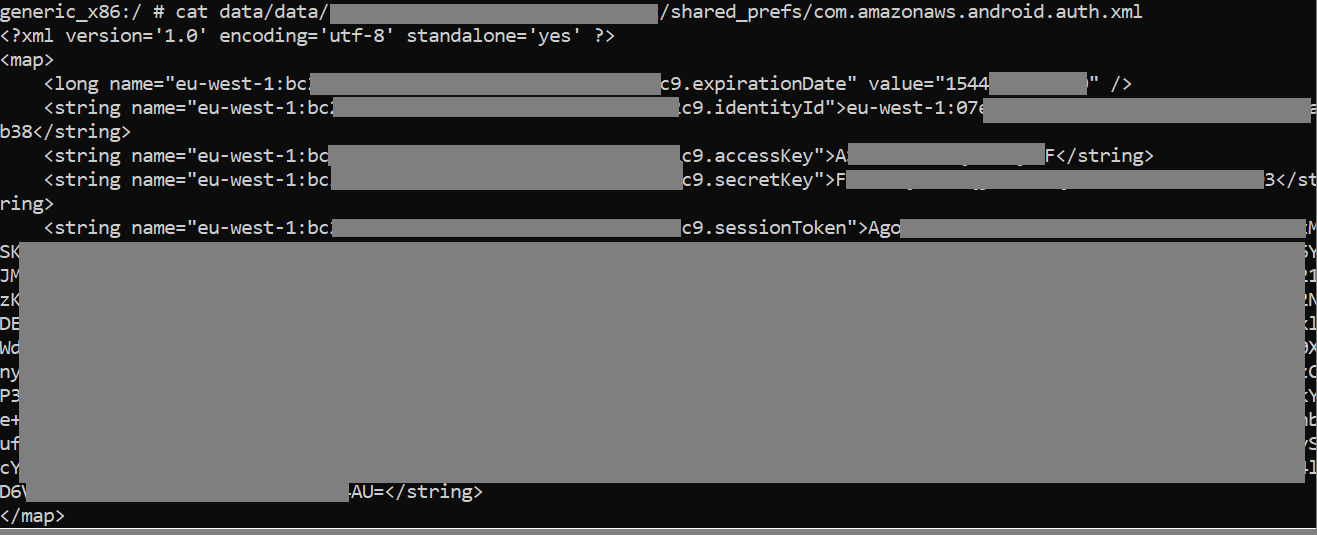
Amazon AWS SDK <=2.8.5 for Android uses Android SharedPreferences to store plain text AWS STS Temporary Credentials retrieved by AWS Cognito Identity Service. An attacker can use these credentials to create authenticated and/or authorized requests. Note that the attacker must have "root" privilege access to the Android filesystem in order to exploit this vulnerability (i.e. the device has been compromised, such as disabling or bypassing Android's fundamental security mechanisms).
Impact#
No impact statement in the source data.
Weaknesses#
No weakness recorded in the source data.
References#
- https://raw.githubusercontent.com/lorenzodifuccia/cloudflare/master/Images/vulns/aws/aws_sdk_sp_01.png
- https://raw.githubusercontent.com/lorenzodifuccia/cloudflare/master/Images/vulns/aws/aws_sdk_sp_02.png
- https://raw.githubusercontent.com/lorenzodifuccia/cloudflare/master/Images/vulns/aws/aws_sdk_sp_03.png
- https://aws-amplify.github.io/aws-sdk-android/docs/reference/com/amazonaws/auth/CognitoCachingCredentialsProvider.html
Exploit#
No public exploit known
History#
- Version 1Record published in the CVE List.
- Version 2Most recent update recorded in the CVE List.